Process Monitor is an advanced monitoring tool for Windows that shows real-time file system, Registry and process/thread activity. It combines the features of two legacy Sysinternals utilities, Filemon and Regmon, and adds an extensive list of enhancements including rich and non-destructive filtering, comprehensive event properties such as session IDs and user names, reliable process information, full thread stacks with integrated symbol support for each operation, simultaneous logging to a file, and much more. Its uniquely powerful features will make Process Monitor a core utility in your system troubleshooting and malware hunting toolkit.
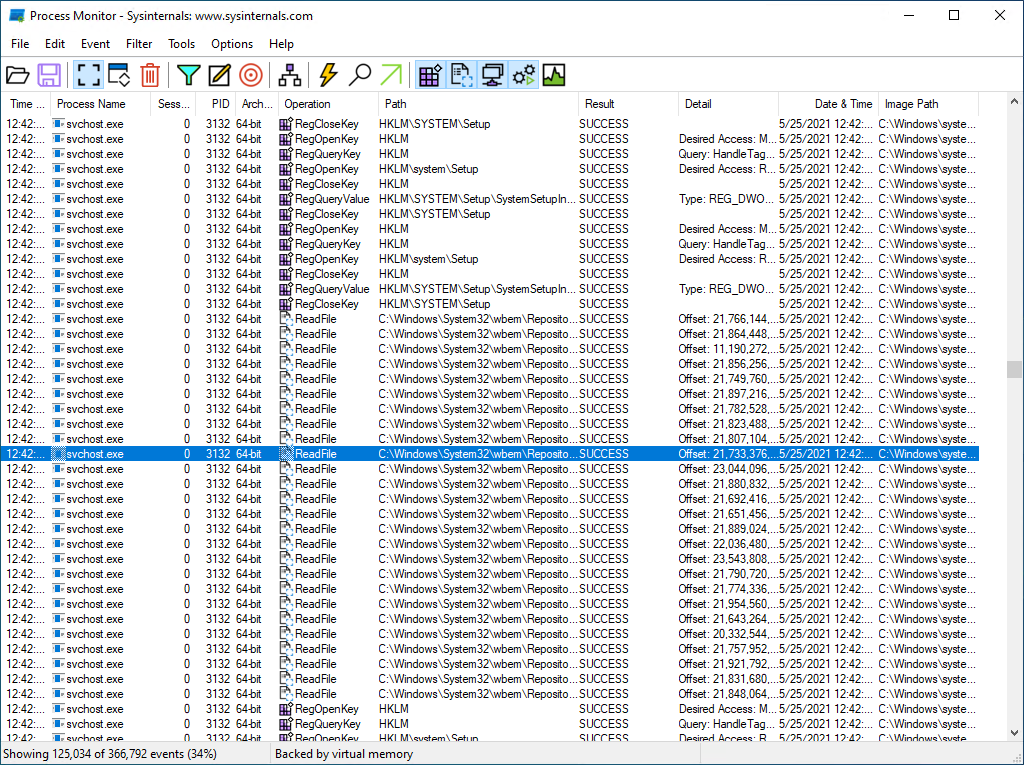
Overview of Process Monitor Capabilities
Process Monitor includes powerful monitoring and filtering capabilities, including:
- More data captured for operation input and output parameters
- Non-destructive filters allow you to set filters without losing data
- Capture of thread stacks for each operation make it possible in many cases to identify the root cause of an operation
- Reliable capture of process details, including image path, command line, user and session ID
- Configurable and moveable columns for any event property
- Filters can be set for any data field, including fields not configured as columns
- Advanced logging architecture scales to tens of millions of captured events and gigabytes of log data
- Process tree tool shows relationship of all processes referenced in a trace
- Native log format preserves all data for loading in a different Process Monitor instance
- Process tooltip for easy viewing of process image information
- Detail tooltip allows convenient access to formatted data that doesn’t fit in the column
- Cancellable search
- Boot time logging of all operations
The best way to become familiar with Process Monitor’s features is to read through the help file and then visit each of its menu items and options on a live system.
(Freeware) x86 x64
Download
(Linux) Procmon
Visit
(中文汉化版) x86 x64
该软件由 th_sjy 汉化
捕获操作的输入和输出参数的更多数据
非破坏性过滤器,允许您设置过滤器而不会丢失数据
捕获每个操作的线程堆栈,在许多情况下它可以找出一个操作的根源
可靠捕获进程的详细信息,包括映像路径、命令行、用户和会话 ID
任何事件属性的可配置和可移动列
可将过滤器设置为任何数据字段,包括未配置为列的字段
高级日志记录架构,扩展到数以百万计的捕获事件和千兆字节的日志数据
进程树工具显示在跟踪中引用的所有进程的关系
本机日志格式保存,在不同的 Process Monitor 实例中加载的所有数据
进程工具提示,方便查看进程映像信息
详细信息工具提示,允许方便地访问不适合的列数据格式
可取消搜索
所有操作的启动时间日志